Hi Experts,
I would know if someone have maybe tried.
I have no license for QCAT, the UE log files are opened by QCAT app and not Wireshark.
So what could I do to open UE QCAT files?
(I don’t have QCAT app)
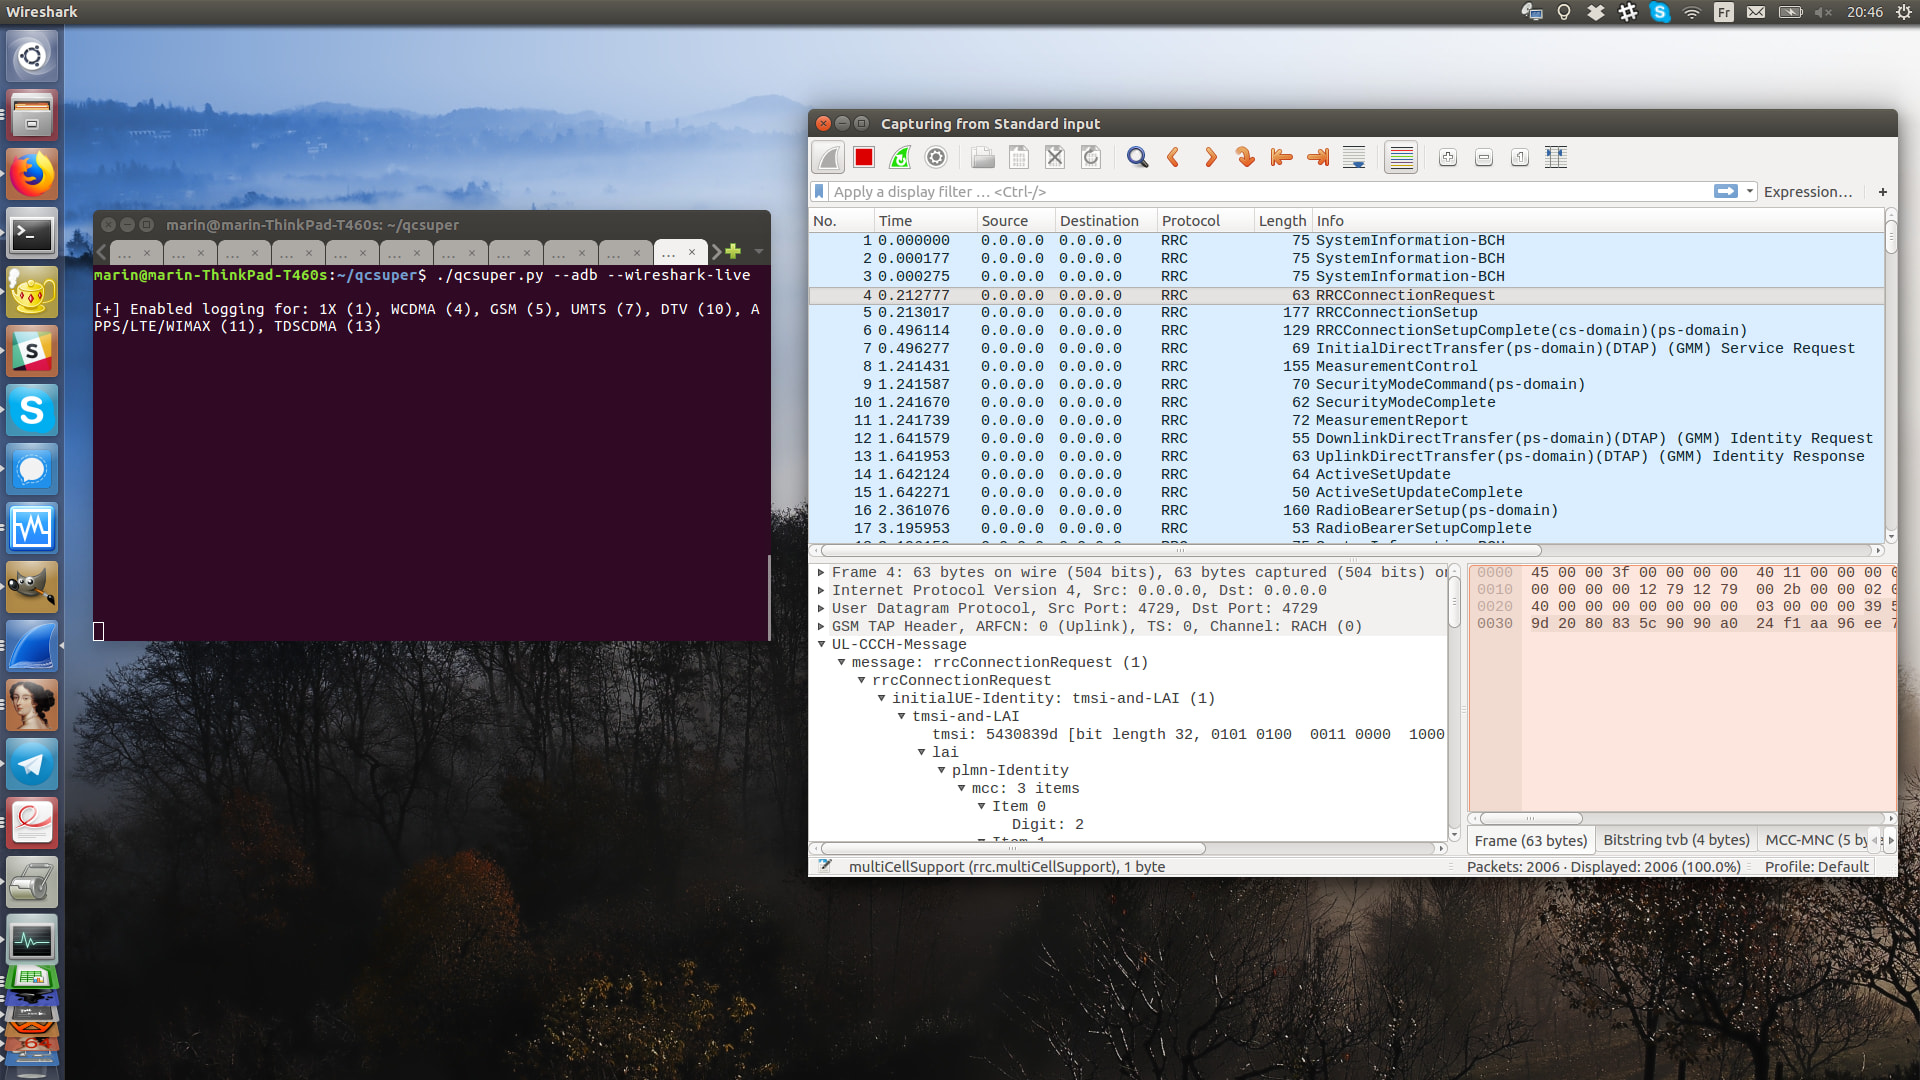
You would need to open first in QCAT and then you can convert to PCAP files.
UE logs can’t be opened directly in Wireshark.
Hi bro, tried to use the tools→ converto to pcap but generated empty text file. Is there any other requirements , maybe license or something else?
The empty output isn’t a license problem — QCAT’s Convert to PCAP only writes the OTA signalling messages (RRC/NAS) it finds in the log. If the diag log was captured without the OTA/signalling log masks enabled, there’s nothing to export → empty file. Also check the Generate-PCAP dialog actually has the technology (LTE/NR) ticked; if none is selected it produces an empty file too.
Fastest fix is to skip QCAT entirely and use SCAT (free, open source — GitHub - fgsect/scat: SCAT: Signaling Collection and Analysis Tool · GitHub ). It reads Qualcomm qmdl / qmdl2 / dlf dumps and writes a GSMTAP pcap straight into Wireshark. For an already-captured file:
python3 scat.py -t qc -d yourlog.qmdl -F out.pcap
Three things that trip people up:
- Wireshark 2.6+ and install SCAT’s Wireshark Lua plugin — without it, LTE MAC/PDCP and NR frames won’t dissect and the capture looks empty even when it isn’t.
- NR RRC / NAS-5GS rides on GSMTAPv3, which isn’t merged into mainline Wireshark yet, so the plugin is mandatory for 5G logs — and keep the original qmdl, because the GSMTAPv3 format is still changing.
- SCAT can’t parse the newer qdss / hdf format some 2021+ chipsets log in. If your file is that format, it’ll also come out empty — confirm you’re on current SCAT master, or re-capture in qmdl.
QCSuper ( GitHub - P1sec/QCSuper: QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things. · GitHub ) is the other free route — more live-capture oriented, but also produces Wireshark-ready GSMTAP pcap.
If you paste what device/chipset produced the log and the file extension, I’ll tell you which path will actually work for it.